FedRAMP release 2026.10.13.01 changed the NIST SP 800-53 control mappings for 40 of 46 Key Security Indicators and 36 requirements. The change is recorded per rule and in git, and is not listed in the published changelog.
CISA added CVE-2026-21589 to the KEV catalog on October 15 with an October 18 federal deadline. Atlassian rejected the CVE record on October 16. The advisory and fix versions remain published; remediation tracking keyed on the CVE ID needs to account for the rejected record.
FedRAMP published the Class D pilot requirements on October 15: two definitions, ten new Key Security Indicators and metric data every four hours. Participation requires a Class C certification dated before December 1 and, after the pilot, six months at Class C without corrective action.
FedRAMP opened a discussion thread on RFC-0035 and RFC-0036. It covered Class G, which does not appear in the rules, and a change that moves Class D cryptography assurance from a requirement to a disclosure. The public certification data has no field for that disclosure.
FedRAMP has no written 60-to-90-day continuous monitoring observation period. The one rule that set an observation floor (six months at Class C, eighteen at Class D) was removed on October 8 as duplicative.
CISA added CVE-2025-61624 to the KEV catalog on October 16 with an October 19 due date. It is rated 6.5 Medium and requires administrator access. Unit 42 reported attackers obtaining admin credentials from exfiltrated config files and using the path traversal to gain root on the appliance.
FedRAMP's agency rules prohibit agencies from requiring additional materials from FedRAMP Certified offerings unless the agency head determines a need and notifies FedRAMP. There is no mechanism for a provider to learn the rule was broken. This post covers the rule and that gap.
FedRAMP confirmed that the independent assessor populates none of the Security Decision Record attributes, and the JSON schema reflects that. A month later, the rule distinguishing Class B from Class C in the record changed.
FedRAMP says whether a Trust Center is part of the cloud service offering depends on MAS-CSO-IIR. If scoped out, it is a third-party information resource with its own documentation, and FedRAMP regulates trust centers in both cases.
Shopify's CEO used the term "slop grenades" for unverified AI output. This post traces one ticket from filing to merge and shows the record kept at each step: what the AI did, on whose instruction, and the result.
The FedRAMP 20x Class B and Class C submission pipelines opened on August 31. Both use the same fifteen rulesets; Class C has shorter timelines. This post compares the two and covers keeping evidence current.
CISA added CVE-2026-59822, an authentication bypass in LiteLLM's MCP endpoint, to the KEV catalog on September 2, due September 16. The fix shipped in a release on May 14. Systems upgraded in June to the version named by the earlier LiteLLM KEV entry are one release short of it.
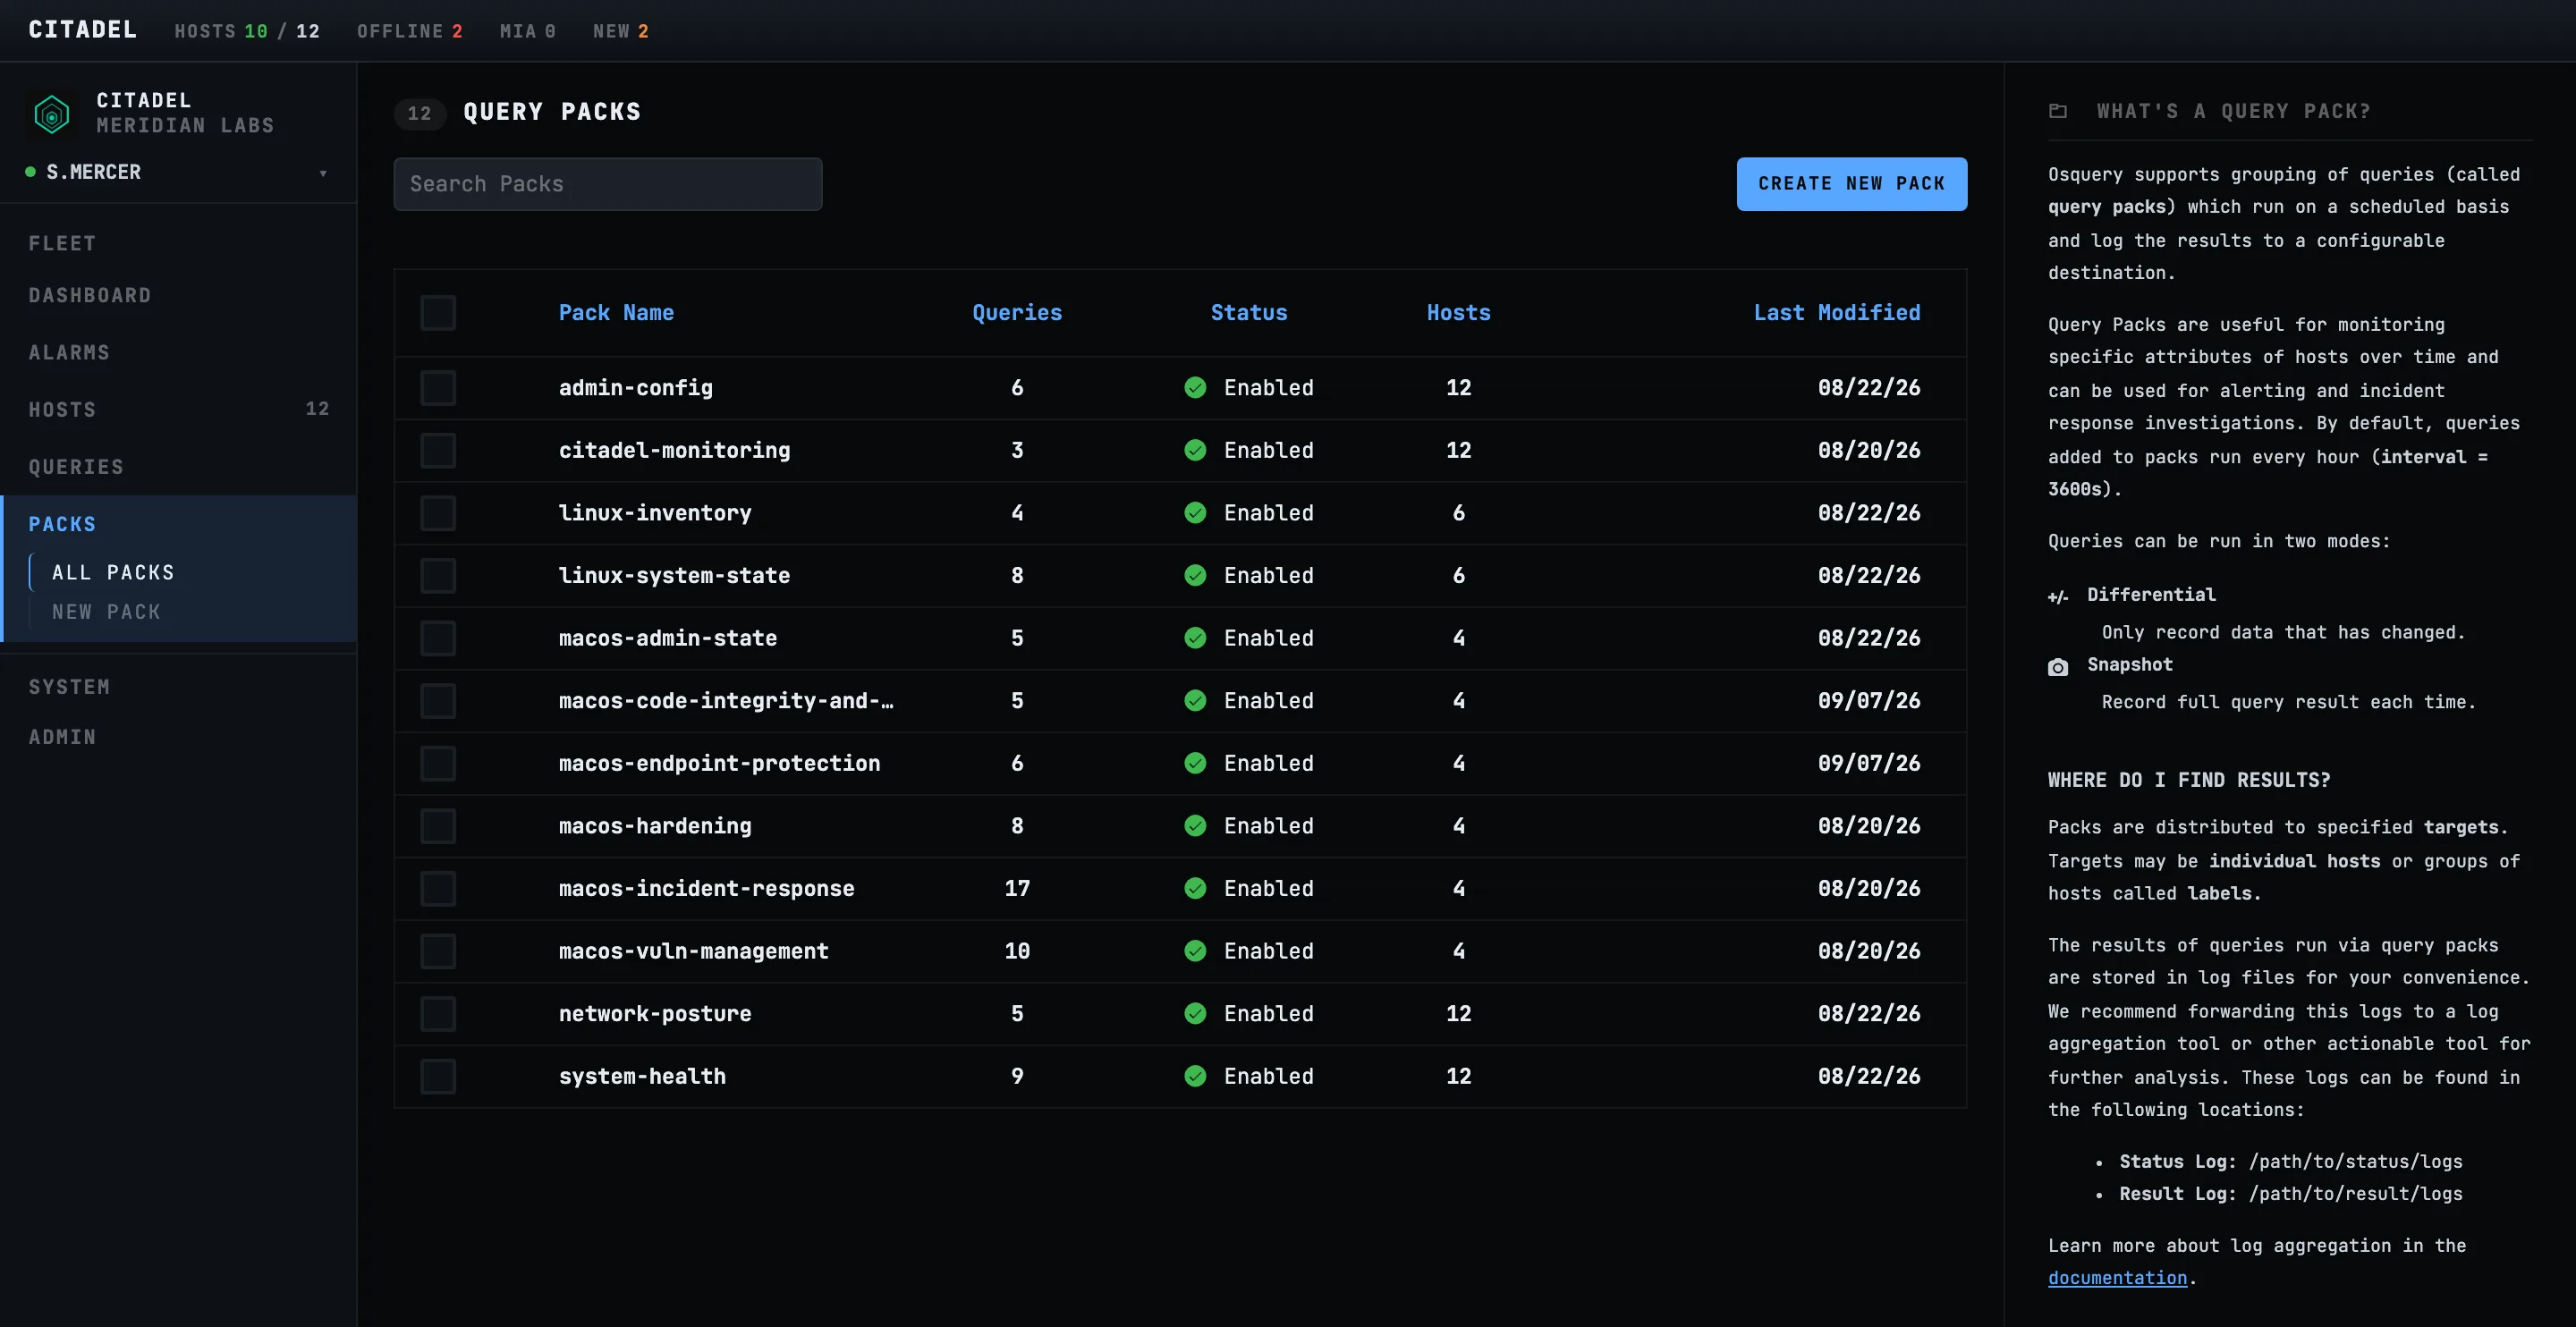
Citadel's pack library now has twelve query packs, covering macOS, Linux and cross-platform posture. This post lists each pack, what it collects and how to read its results.
On August 31 CISA added CVE-2026-81578 and CVE-2026-82078, the two parts of a PaperCut NG/MF exploit chain, to the KEV catalog, due September 14. PaperCut released a third emergency patch the same day; systems on the first or second patch are not protected.
On August 26 CISA added CVE-2026-8452, a memory overflow in NetScaler ADC and NetScaler Gateway, to the KEV catalog with an August 29 due date. It was published June 30 with five related CVEs, all fixed by the same build; only CVE-2026-8452 is on the KEV list.
CISA added CVE-2026-9198 to the KEV catalog on August 4 with an August 7 due date. The entry lists IBM as the vendor; Langflow's five earlier entries list Langflow. Automation that matches on vendor name will miss it.
On August 27 CISA added CVE-2023-49105, an unauthenticated file read/write/delete in ownCloud core, to the KEV catalog with an August 30 due date. It was published and fixed in November 2023. A related CVE from the same advisory was listed in 2023 and fixed by a different artifact, so systems that remediated only that one remain exposed.
CISA added CVE-2026-55040, a JWT authentication bypass in on-premises SharePoint, to the KEV catalog on August 18 with an August 21 due date. The patch was available July 14, and CISA records exploitation from July 13, 36 days before the listing.
CISA added CVE-2026-50522, an unauthenticated deserialization RCE in SharePoint, to the KEV catalog on July 22 with a July 25 due date. The fix builds are the same ones that fixed the July 14 SharePoint KEV item. This post covers recording remediation evidence by build.
CISA added CVE-2026-20316, a hard-coded password in Cisco Secure Firewall Management Center, to the KEV catalog on July 29 with an August 1 due date. NVD scores it 5.3; Cisco rates it High. Use of the credential appears as a normal login.
CISA added CVE-2026-64849, an unauthenticated SSRF in MLflow's webhook test endpoint, to the KEV catalog on August 19, due September 2. It scores 9.3; CISA's SSVC rates technical impact as partial. MLflow is typically installed with pip, outside vendor advisory subscriptions.
CISA added CVE-2025-68686 to the KEV catalog on July 27 with an August 10 due date. Rated 5.9 Medium, it bypasses the April 2025 fix that removed an attacker's SSL-VPN symlink, so systems remediated then need re-checking.
CISA added CVE-2026-0770, unauthenticated remote code execution as root in Langflow, to the KEV catalog on July 21 with a July 24 due date. It is Langflow's fifth KEV entry and the third in the same code-validation endpoint. It was public and unfixed for six months before the listing.
CISA's July 16 KEV batch included two unauthenticated command injections in Fortinet FortiSandbox. CVE-2026-25089 also affects FortiSandbox Cloud and PaaS, which are vendor-operated. This post covers inherited responsibility for those variants.
On July 15 CISA added CVE-2023-4346, an account-lockout flaw in the KNX building-automation protocol, to the KEV catalog with a July 29 due date. An attacker can lock operators out of KNX devices by setting a BCU key. This post covers whether building systems fall inside the authorization boundary.
CISA added CVE-2026-39808, an unauthenticated OS command injection in Fortinet FortiSandbox, to the KEV catalog on July 16 with a July 19 due date. This post covers determining whether security appliances are inside the authorization boundary.
CISA added CVE-2026-56164, a missing-authentication flaw in on-premises SharePoint Server that allows unauthenticated privilege escalation, to the KEV catalog. NVD scores it 9.8; Microsoft scores it 5.3. This post covers scoping SharePoint farms against the authorization boundary.
CISA added CVE-2026-55255, an authorization bypass in Langflow, to the KEV catalog on July 7 with a July 10 due date. An authenticated user can access other users' flows, which breaks tenant isolation.
FedRAMP's 2026 transition calendar: Marketplace listings for 20x open July 6, FedRAMP Ready becomes Legacy July 28, Class A opens August 3, Classes B and C open August 31, and existing Rev5 systems adopt the new rules by January 1, 2027.
On July 1 CISA added CVE-2026-45659, a deserialization RCE in on-premises SharePoint Server, to the KEV catalog with a July 4 due date. Microsoft patched it in late May and rated it "Exploitation Less Likely." This post covers how advisory exploitability ratings relate to FedRAMP's assume-automatable rule.
A June 22 executive order sets federal post-quantum cryptography deadlines (encryption by 2030, authentication by 2031) and applies them to contractors through the FAR. It also requires a cryptographic bill of materials. This post covers starting the cryptographic inventory now.
OMB M-25-21 requires each agency to name a Chief AI Officer, publish an AI use-case inventory and apply minimum risk practices to high-impact systems. As of April, 56 agencies reported 3,611 use cases, 445 of them high-impact.
CISA's BOD 26-04 replaces CVSS-ordered patching with four risk questions (exposure, automatability, control granted, active exploitation) and urgency tiers from three days to fix-on-upgrade. FedRAMP's NTC-0014 aligns to it and adds a rule: treat every exploit as automatable unless proven otherwise.
On June 23 CISA added three Ubiquiti UniFi OS flaws to the KEV catalog: an access-control bypass under active exploitation, a path traversal and a command injection. Chained, they lead from network access to command execution on the device.
CISA added CVE-2026-42271, a command injection in the LiteLLM AI gateway, to the KEV catalog on June 8 with a June 22 due date. The injection is in two MCP preview endpoints; chained with a Starlette host-header bypass, it allows unauthenticated RCE.
Under the Consolidated Rules for 2026, "FedRAMP Authorized" becomes "FedRAMP Certified," and the Low, Moderate and High baselines become Certification Classes A, B, C and D. This post covers which changes are naming only and which change requirements.
On June 2, CISA added CVE-2022-0492, a container-escape bug in the Linux kernel's cgroups code, to the KEV catalog. This post covers what it means for AI agents isolated only by containers.
CISA added CVE-2026-0257, an authentication bypass in Palo Alto PAN-OS GlobalProtect, to the KEV catalog on May 29 with a June 1 due date. Only on-prem GlobalProtect is affected; Cloud NGFW and Panorama are not. This post covers checking boundary scope first.
GSA has confirmed FedRAMP 20x as the permanent authorization model, now in Phase 3. The Consolidated Rules for 2026 finalize by the end of June, take effect July 1 and run through 2028, with the submission pipeline opening in Q4.
CISA added CVE-2025-34291, a CVSS 9.4 account-takeover-to-RCE chain in Langflow, to the KEV catalog on May 21 with a June 4 due date. This post covers including AI orchestration platforms in ConMon scope.
A browsable Rev 5 Moderate and 20x KSI catalog is live at /fedramp/controls. It is the catalog the Novaprospect audit engine evaluates AWS environments against. The engine is in alpha with one collector (IAM) and one evaluator (AC-2).
The 20x Phase One pilot draft submission window runs through May 26, with formal submissions starting May 30. This post covers the preparation work for a machine-readable package.
CISA added CVE-2026-20182, a CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN Controller and Manager, to the KEV catalog on May 14 with a May 17 due date. This post covers the FedRAMP ConMon response on a 72-hour deadline.
FedRAMP published the public preview of its Consolidated Rules for 2026 on May 4. Templates are replaced by machine-readable artifacts, Balance Improvement Releases become mandatory, and Rev 5 and 20x run in parallel through 2028.
Long-lived API keys in AI agent environments carry the same risk as plaintext production credentials. This post covers short-lived, scoped credentials for agents.
An AI gateway, such as Vercel's, routes all model traffic through one point. This post covers using that point for compliance controls: logging, policy enforcement and provider restrictions.
Computer-use APIs let a model operate a desktop through screen, keyboard and mouse. Network-layer air gaps do not stop a model that can type. This post covers the controls that apply.
Anthropic's 1M-token context window affects data minimization, audit log volume and exfiltration exposure. This post covers the compliance changes to plan for.
AI systems send portions of stored data to model providers on each inference. This post covers tracking where that data is processed to meet data residency commitments.
Egress policies built for conventional workloads do not account for AI agents that fetch URLs and call external APIs. This post covers what egress control for agents needs to include.
Automated evidence collection for continuous monitoring exposes gaps between compliance artifacts and the controls they describe. This post covers closing those gaps.
Model red teaming tests for jailbreaks. Agentic-system red teaming tests sequences of tool actions that lead to damage. This post covers the differences in scope and skills.
An AI workload that calls an external model provider crosses the FedRAMP authorization boundary on each request. This post covers how to account for that in boundary documentation.
An AI agent with a URL-fetching tool can be used to move data out of a network without compromising the model. This post covers how the attack works and the controls that limit it.
AI agents at Novaprospect cannot commit to main. This post covers the branch rules we apply to agents and why they are stricter than the rules for human engineers.
SOC 2 has no AI-specific Trust Services Criteria; the existing criteria apply. This post covers the AI-related questions auditors are asking and the evidence that answers them.
Audit trails designed for human engineers do not scale to agentic workflows. This post covers structuring agent audit logs so they remain usable at that volume.
The practices used in regulated engineering, such as change control, review and audit trails, apply directly to AI-assisted development. This post covers how we apply them.
Amazon's AI coding tool reportedly deleted a production environment, causing a 13-hour AWS outage; Amazon attributed it to user error. This post covers the permission and review controls that apply to AI coding tools.
FedRAMP 20x shortens authorization paths and reduces documentation by up to 80%. This post covers the increase in authorization volume that is expected and what mid-market CSPs need in place.