Novaprospect products

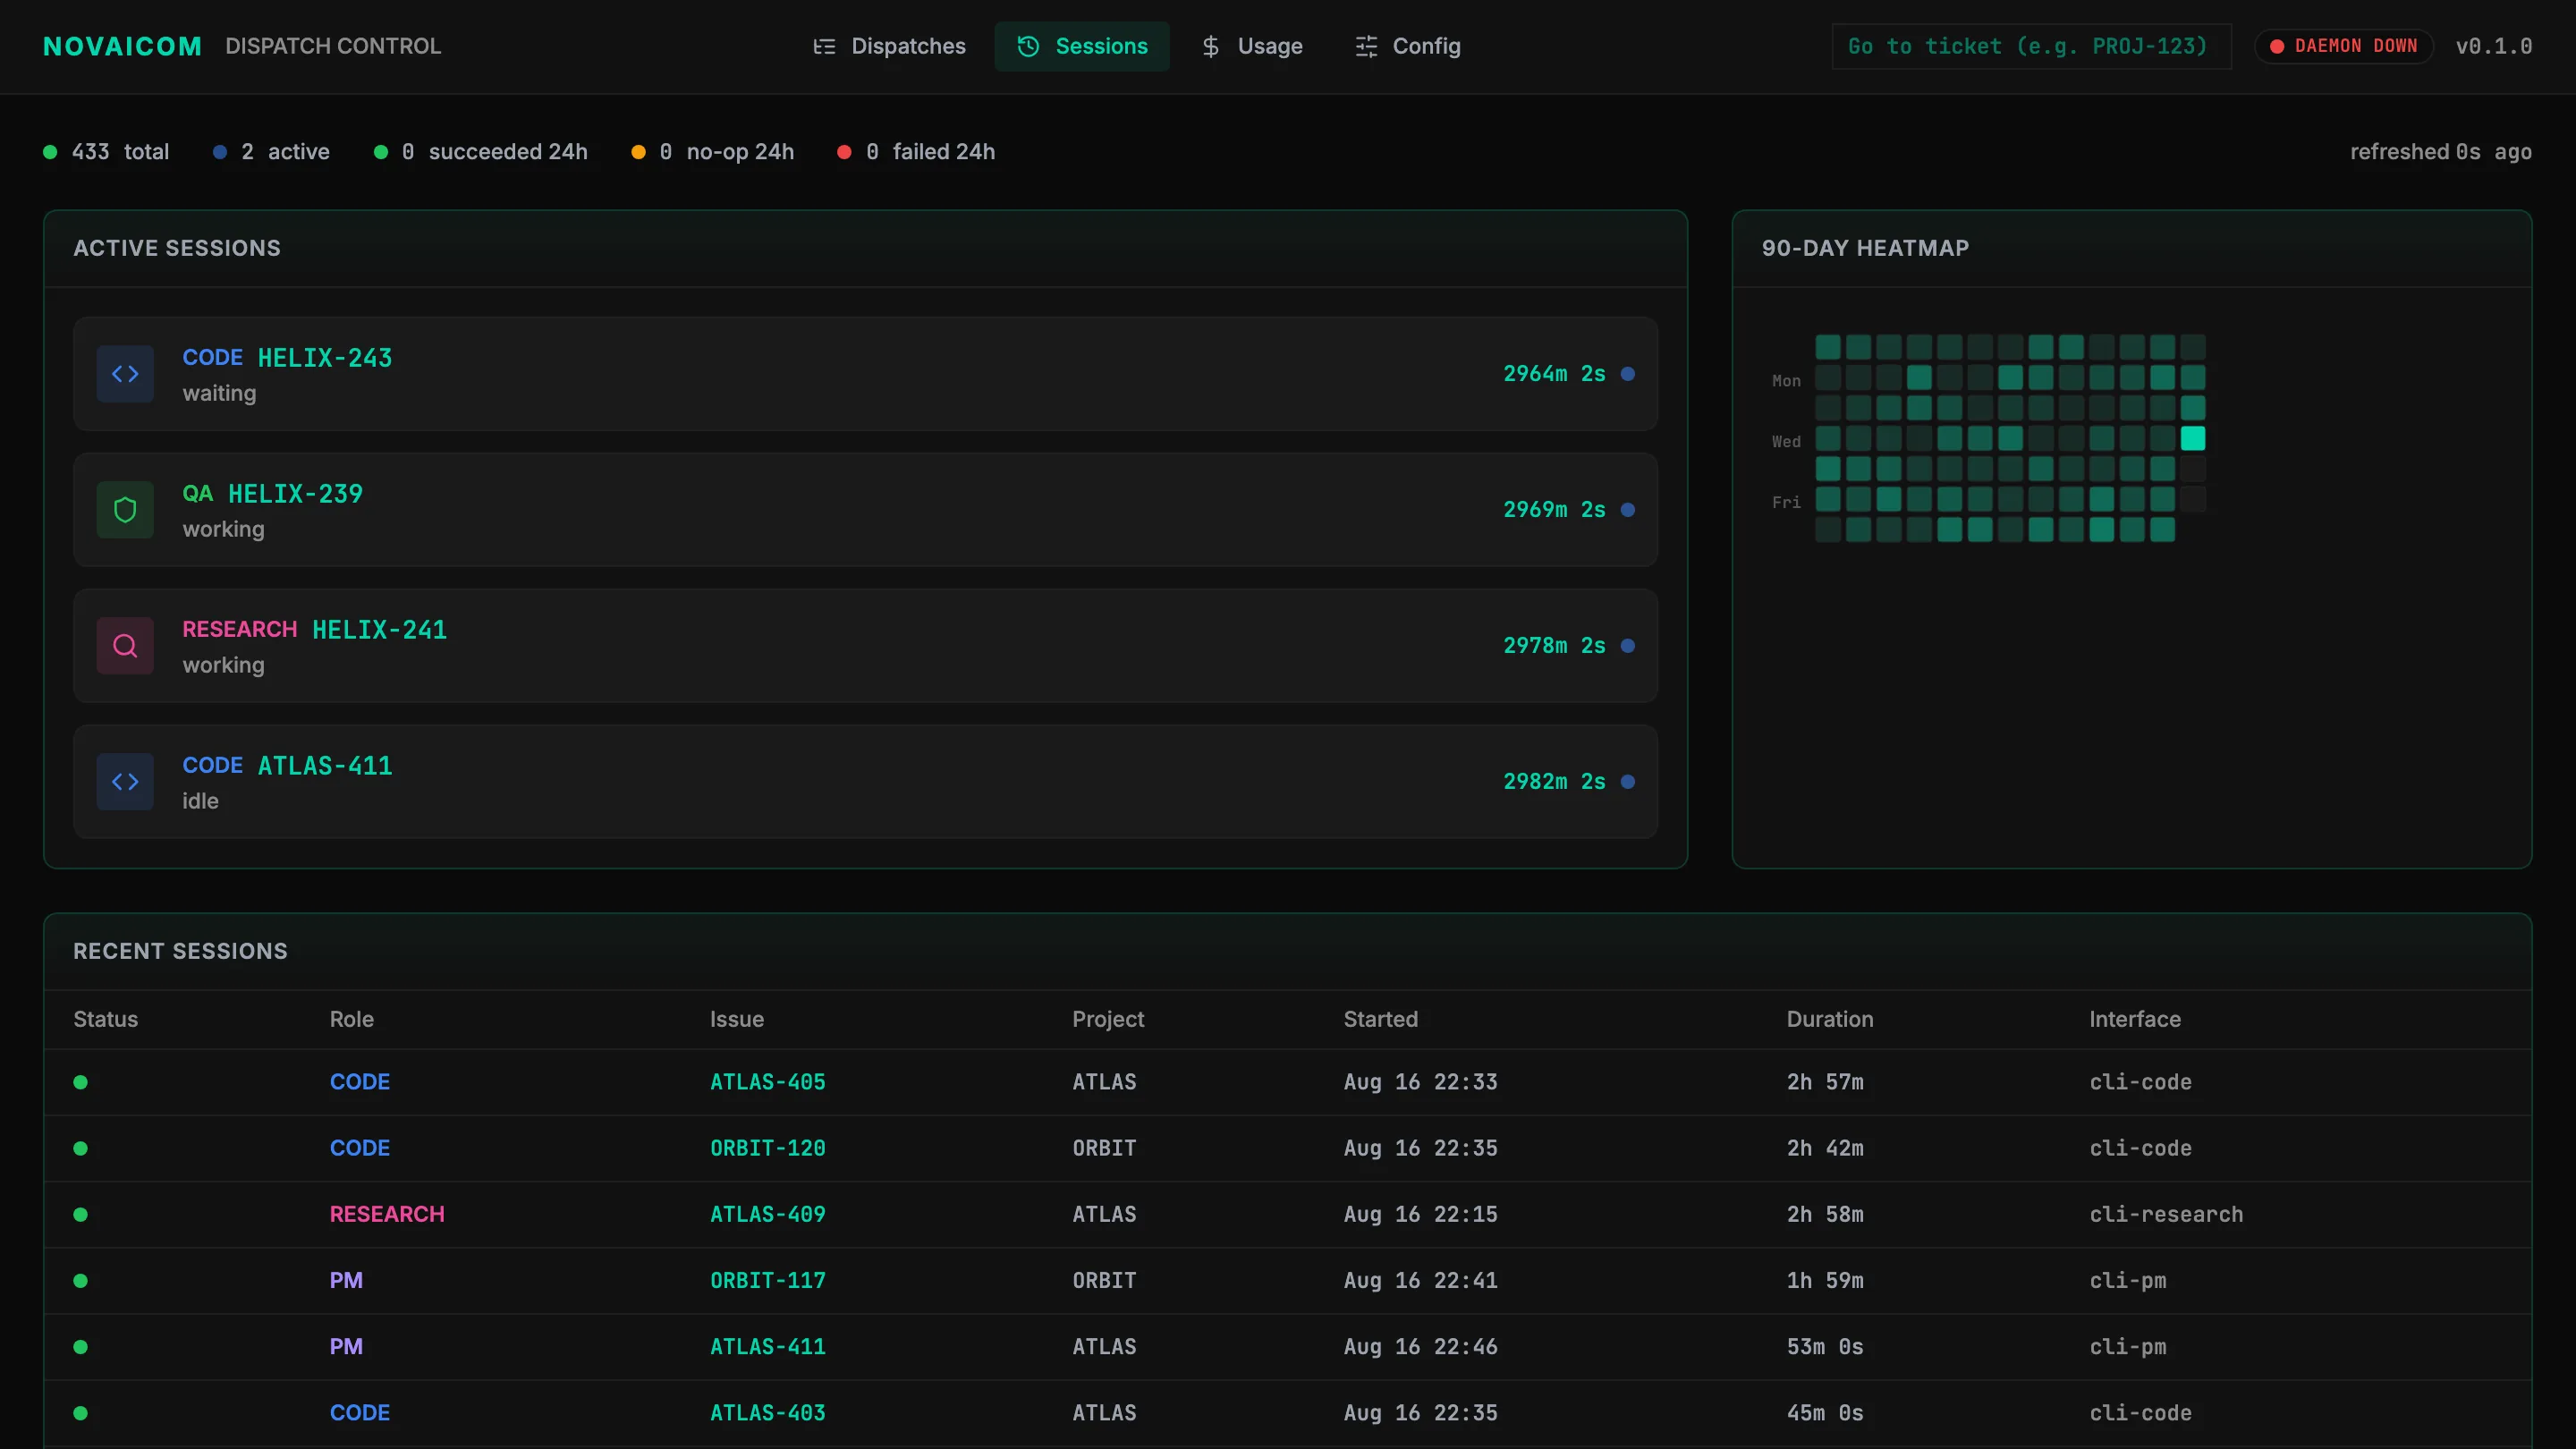
The NAICOM sessions view: a counter strip reading total and active sessions, an active-sessions panel listing code, QA and research runs each against an issue key, a 90-day activity heatmap, and a recent-sessions table.
Generally available

NAICOM

The audit trail for AI-assisted engineering.

NAICOM sits between your engineers and the models they work with, and writes down what happened. Every session opens against a tracked issue. Every instruction is a versioned prompt file committed beside the code it produced. Every commit carries the session ID, the issue key, and the human who approved the merge — so "which of these changes was AI-written, and on whose authority?" is a query. It runs against the forge you already use — GitHub, GitLab, Bitbucket or Gitea, resolved per repository — so nothing about the existing workflow has to move.

The screen above is a demo tenant; the customer and its sessions are invented.
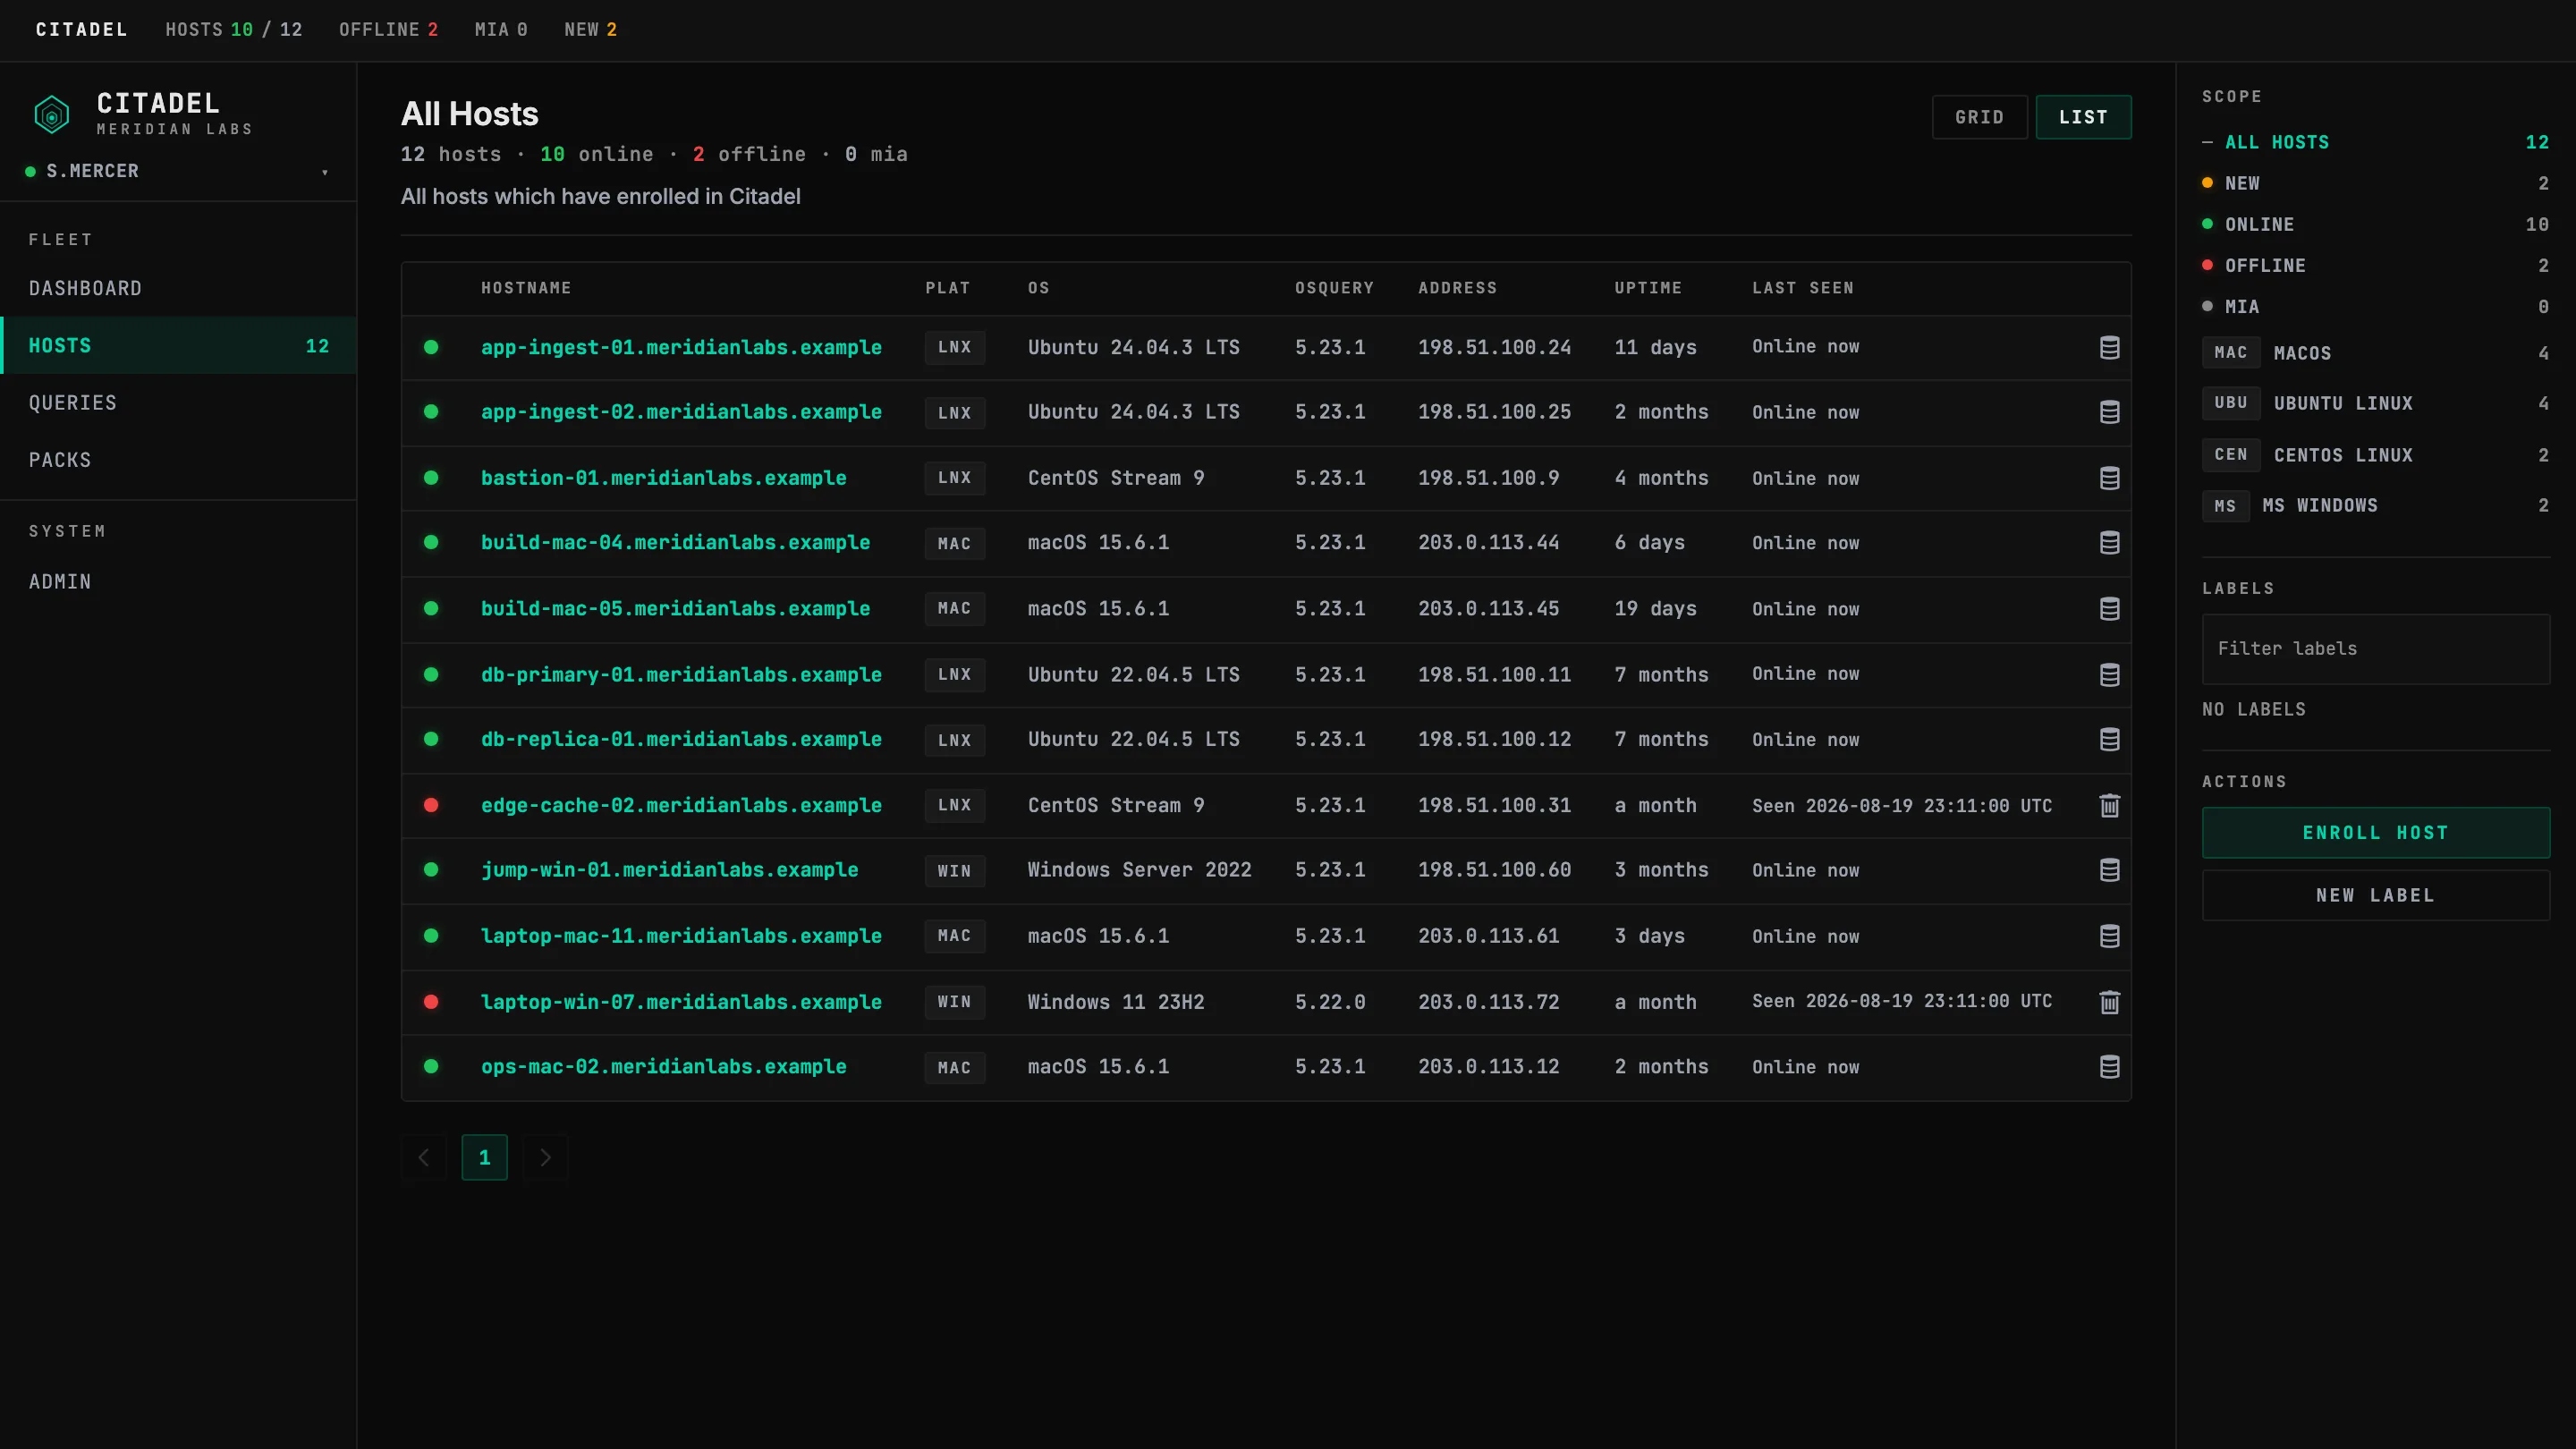
The Citadel hosts view: a table of twelve enrolled hosts with per-row status dot, hostname, platform tag, operating system, osquery version, address, uptime and last-seen time; a scope panel counting 12 all hosts, 10 online, 2 offline, 0 mia, and the built-in macOS, Ubuntu, CentOS and Windows labels.
Version 1.0.0 · generally available

Citadel

Live host-state evidence for regulated fleets.

Citadel is a host-state evidence platform for regulated environments. It enrols and configures the Citadel agent across a host fleet, distributes compliance-aligned query packs, and turns their results into a signed, append-only evidence stream — so "what is actually running on every host, and what was running on the day of the finding" is a SQL question with a timestamped answer.

Built for fleet-scale collection over mutually authenticated TLS, with packs distributed per platform and every result signed at the agent. Air-gap and FIPS 140-3 capable.

The screen above is the control plane running against an example fleet, not a customer's.

Federal compliance tooling

Built for the FedRAMP 20x pathway and the Rev 5 baseline underneath it.

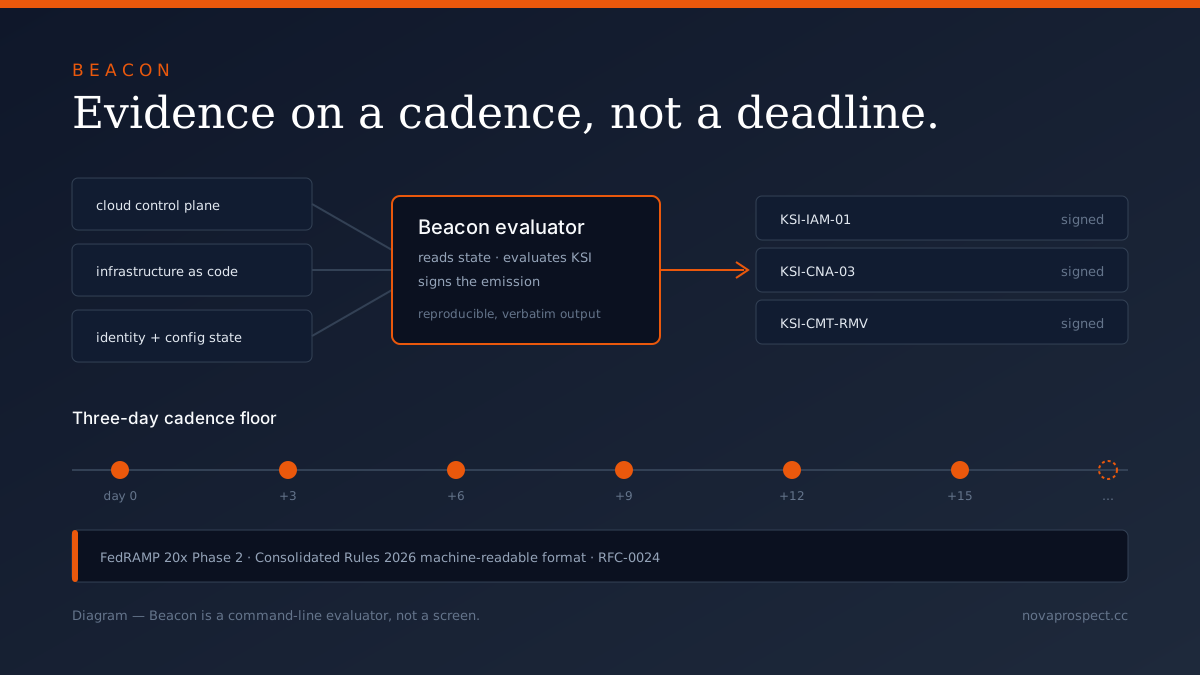
Diagram: cloud and infrastructure-as-code inputs read into the Beacon evaluator, which emits signed KSI evidence — KSI-IAM, KSI-CNA, KSI-CMT — on a repeating three-day cadence timeline.
Beta

Beacon

The continuous KSI emitter for FedRAMP 20x.

Beacon reads infrastructure state continuously and emits signed, machine-readable Key Security Indicator evidence — at the three-day cadence 20x asks for and in the format the Consolidated Rules 2026 mandate. It plugs into the FedRAMP Management Engine or stands alone against your own package.

Designed to emit KSI evidence at the three-day 20x cadence from cloud primitives and IaC it reads directly. The open-source evaluator produces verbatim, reproducible output today.

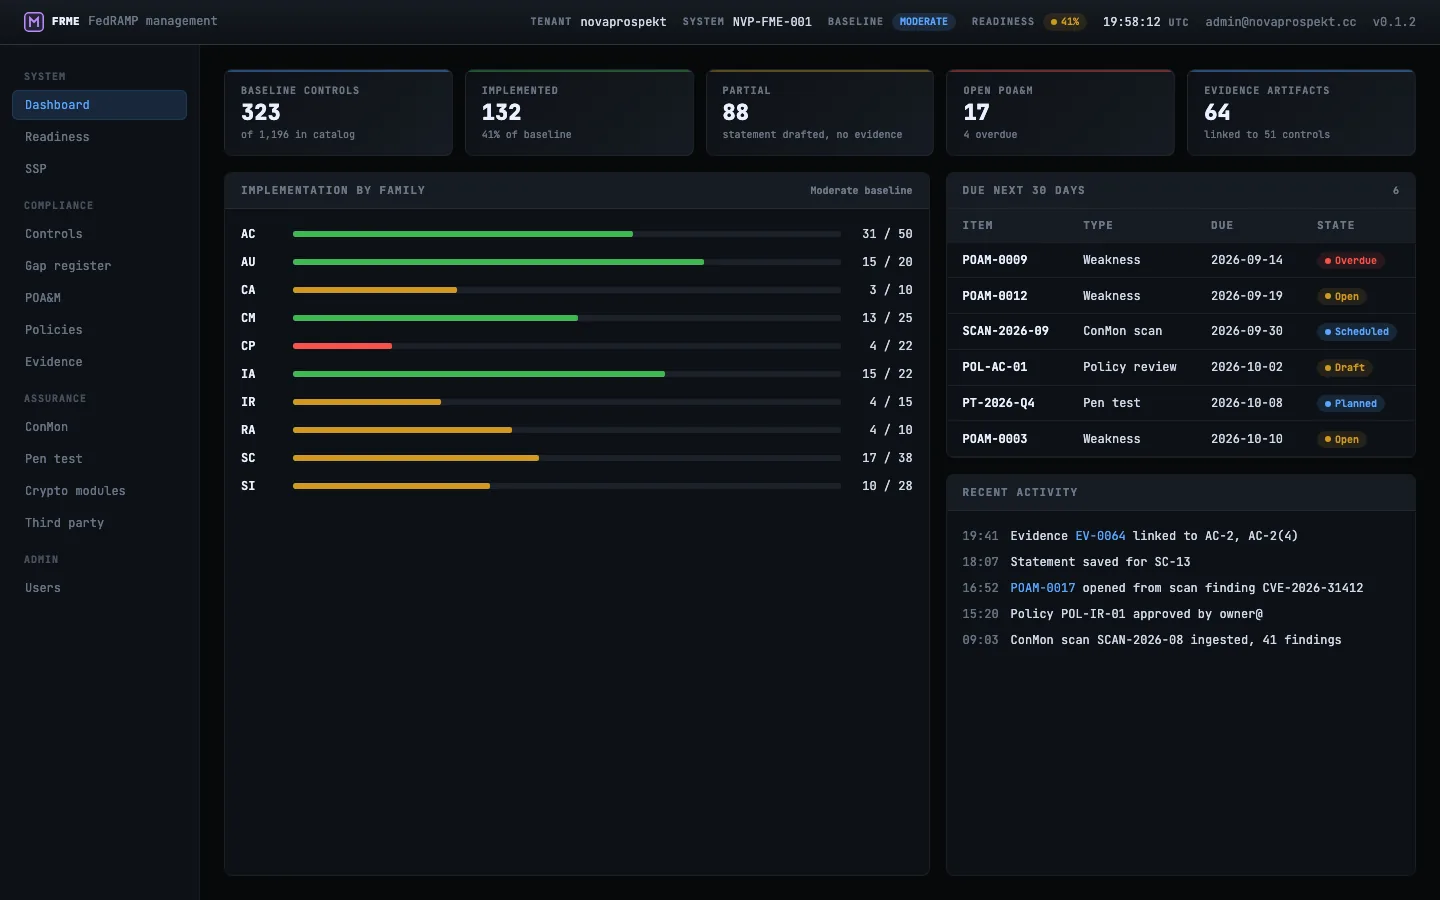
The Engine's dashboard for a system on the Moderate baseline: cards counting baseline controls against the catalog, controls implemented, controls with a statement but no evidence, open POA&M items and evidence artifacts; an implementation-by-family panel giving each 800-53 family a progress bar and an addressed-over-applicable count; a table of obligations due in the next thirty days with each item's type, date and state; and a timestamped activity log of evidence links, saved statements, POA&M openings, policy approvals and ingested scans.
Limited release

FedRAMP Management Engine

The system of record for authorization, in both directions.

The Engine holds Beacon's 20x KSI emissions as the authoritative package, and generates Rev 5 OSCAL artifacts and POA&M lifecycle for organizations still on the traditional path through the Consolidated Rules transition window. One record, whichever pathway an authorization is on.

Designed to carry a full Rev 5 Moderate baseline as OSCAL, with POA&M lifecycle and evidence origin references sourced from Beacon and Citadel rather than re-keyed.